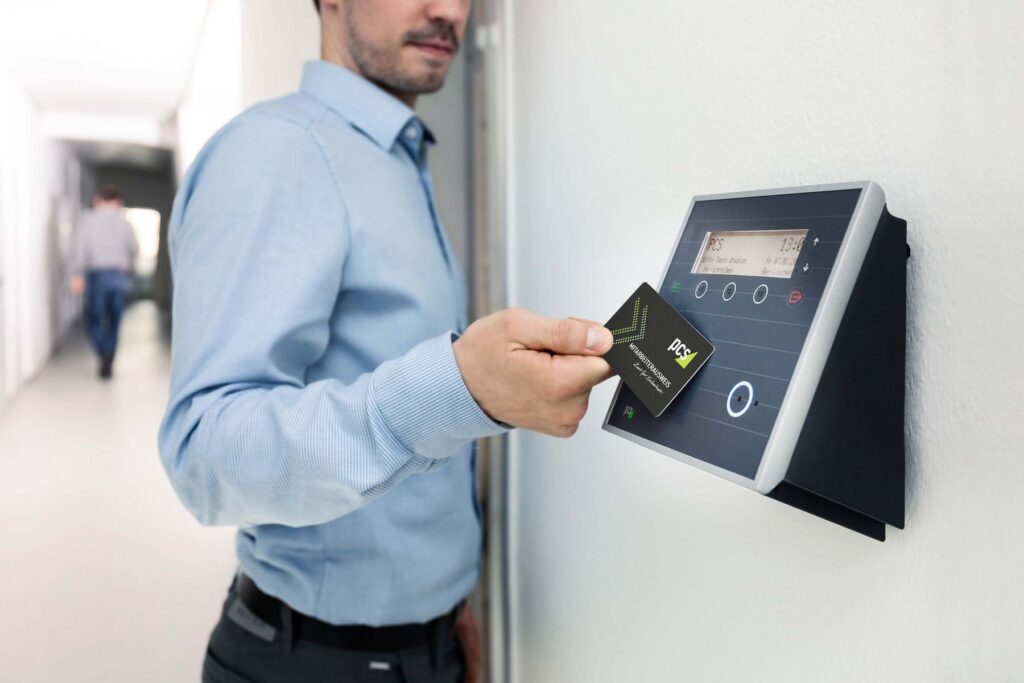
A facility with multiple operational areas cannot be managed only by distinguishing between open and closed doors. Employees, managers, external technicians and suppliers have different needs, often linked to schedules, roles and routes. Access control must translate this organization into understandable and maintainable rules. Each exception must have a duration, an owner and a recognizable procedure.
In this demonstrative project the focus is on the flows. Before choosing readers or credentials, user groups, reserved areas and exceptions are defined. In this way each component follows a real procedure and the system does not become a repository of authorizations that are hard to interpret.
The need
The facility includes common areas, operational departments and rooms accessible only to specific staff. Some suppliers must enter within agreed time slots, while managers need broader routes. The system manager must be able to modify or revoke a credential without affecting all other users.
It is also necessary to consider the physical behavior of the openings. Locks, doors, automations and escape routes have their own requirements that cannot be replaced by electronic authorization alone. Recorded events must be proportionate to the purpose and viewable exclusively according to the responsibilities defined by the owner. Management must remain simple and verifiable.
The designed solution
The initial analysis maps people, roles, schedules and passages. The rules are simplified into a few recognizable profiles, including non‑ordinary situations: new hires, lost credentials, temporary visits and maintenance accesses. This work precedes the choice of identification method.
For each gate, the reader, actuator and behavior under different conditions are defined. Interfaces with automation or other systems are assessed based on compatibility and operational benefit. The configuration assigns authorized administrators and limits data collection to what is needed for the intended management.
The testing includes allowed and denied access trials, credential revocation and notification verification. Responsible parties participate in the tests to compare technical behavior with internal procedures and correct any impractical rules.
A system designed for everyday use
The concrete advantage is the ability to adjust authorizations without replacing all keys or distributing indistinct accesses. This flexibility, however, requires orderly management: delivery, modification and revocation of credentials must have responsible persons and documented steps.
Simple profiles reduce errors and make it easier to verify who can access a given area. When departments or schedules change, the rules can be reviewed starting from the existing structure. The project thus remains linked to the organization instead of accumulating exceptions over time.
To set up access control correctly, it is advisable to start from a list of roles, gates and schedules, including temporary cases and management responsibilities from the beginning.